





Gathering more information about existing and potential customers is critical to marketing and sales. However, the chronic collection and retention of all that personal data has begun to raise privacy red flags. In general, businesses won’t make expensive changes to infrastructure or procedures just on principle (e.g., “we should protect others’ privacy.”). To rectify, CISOs must find a business reason to make these changes before an incident occurs. Where should the conversation start?
This week’s episode is hosted by me, David Spark (@dspark), producer of CISO Series and Amy-Steagall-Hess, CISO, Stanford University. Joining us is Michael Tran Duff, CISO, data privacy officer, Harvard University.
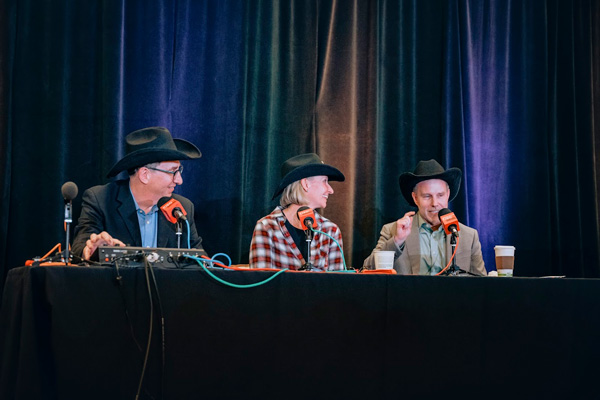
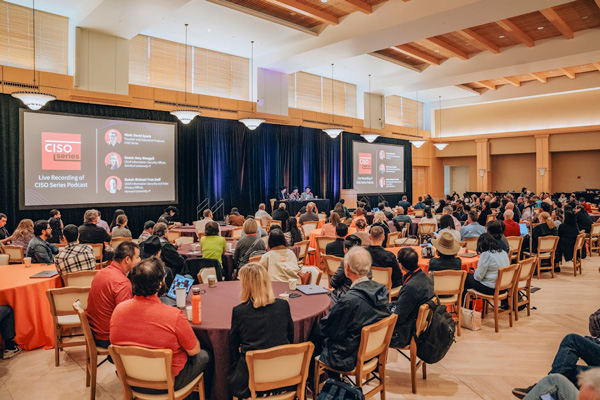
This episode was recorded in front of a live audience at Stanford University as part of their annual Cyberfest event. Check out all these photos from the event.
Got feedback? Join the conversation on LinkedIn.
Huge thanks to our sponsors, Vorlon Security and Wiz
Full transcript
Intro
0:00.000
[Voiceover] Biggest mistake I ever made in security. Go!
[Michael Tran Duff] Two big mistakes in one shot. Issuing a mandate without consultation, 2013, here at Stanford. We were working on this big initiative that affected all the faculty. I failed to consult the faculty, and worse yet, we called it a mandate. So, I failed to anticipate the reaction that would have, but the good news is we were able to work closely with the faculty and make adjustments to the program.
[Voiceover] You’re listening to CISO Series Podcast, recorded in front of a live audience.
[Audience] At Stanford!
[Applause]
[David Spark] Welcome to the CISO Series Podcast. My name is David Spark, I’m the producer of the CISO Series. Joining me to my left is my guest co-host for this episode. It is Amy Steagall-Hess, the CISO of this very university, Stanford. Let’s hear it for Amy.
[Applause]
[David Spark] So, great you’re here, Amy.
[Amy Steagall-Hess] Happy to be here, David, and thank you for joining us.
[David Spark] All right, so we are live at Stanford. This is part of the CyberFest event. By the way, I do want to mention our sponsors that we’ll be talking about later in the show, Wiz and Vorlon. Let’s hear it for Wiz and Vorlon for making this possible.
[Applause]
[David Spark] Now, I didn’t mention this to you. We had dinner last night, and I mentioned this is not the first time I’ve performed on Stanford campus. I actually performed once before. I used to work as a stand-up comedian many, many years ago, and I had a gig right here. I was working with some of you may know the comedian Don McMillan. He is often known as the PowerPoint comedian. I was working with him here. This goes back many, many years ago. He actually won Star Search, give you an idea how long ago that was. But he also was recently on America’s Got Talent as well, but he did not win that as well. But here’s the thing that I very vividly remember of coming here to Stanford the first time and performing here was the tour. The young woman who’s showing us around said, “Oh yeah, over there, that’s where they have windsurfing on campus.” That blew my mind. Windsurfing. By the way, do you still have windsurfing on campus? No? It’s gone?
[Michael Tran Duff] Lagunita I thinkdried up.
[David Spark] It did dry up? Oh, was it on a lake that dried up?
[Michael Tran Duff] I believe so.
[David Spark] You can talk in the microphone. Yeah, speak up. This is Michael.
[Laughter]
[David Spark] This is Michael. I was going to introduce him in a second. This is Michael Tran Duff, CISO of Harvard. Let’s hear it for Michael.
[Applause]
[Michael Tran Duff] It’s great to be back here at Stanford, the Harvard of the West.
[Laughter]
[David Spark] So, what happened to that lake?
[Michael Tran Duff] Well, I know it dried up. I’m looking around because others know much better than I do what happened. But it used to be a full lake, but it just dried up. And then I think there was some indigenous species that started growing, and they were unable to refill the lake for fear of eradicating that.
[David Spark] So, that ended the windsurfing on campus.
[Michael Tran Duff] I think so.
[David Spark] Anyways, when I heard that, my reaction was why does anyone leave the school for any reason?
[Laughter]
Here’s another arrow in the Zero Trust quiver.
3:23.200
[David Spark] Administrative software is the most unsafe part of any organization, claimed Andy Ellis on CSO Online. Now, referencing the calamities of SolarWinds and CrowdStrike, the software used by safety and security teams puts us all at a lot of risk. Do we have much choice? Or is that a risk we always accept in using them? Now, Andy argued that this means it’s time we applied, get ready for this, zero trust models against our own IT, with endpoints not inherently trusting the employer’s ecosystem. I’m going to start with you, Amy, on this. That seems like a super big pill to swallow for many organizations. Is there a middle ground, or do you think you could actually do that?
[Amy Steagall-Hess] So, I think it is a super big pill to swallow. And I think in an academic research environment like this one, we absolutely need to incorporate certain pieces, the good pieces of zero trust, but at the same time, we also need flexible solutions to allow our researchers to continue to do the great work that they do and not impede the way that they actually do their work.
[David Spark] All right, Michael, your take on this? I mean, it sounds like an interesting theory. In practice, I don’t know how you could pull this off.
[Michael Tran Duff] Exactly. That’s what I was going to say, David. I don’t know how you would do this. I do want to say I’m a strong proponent of zero trust. I think it’s as fundamental as the confidentiality, integrity, and availability triad. But when it comes to security tools, what matters most is the net benefit. CrowdStrike has saved our bank in more times than we can count. So, it’s saved us infinitely more times from incidents than incidents that it has caused. We need to remember that. And anytime you have a piece of software that’s broadly installed, it’s a risk.
[David Spark] So, let’s get back though to the discussion of zero trust because it’s a really hot buzzword that really unnerves a lot of people because it’s an absolute, and it’s like reaching some Garden of Eden of cybersecurity. But the thing is, when you start talking about the theories, they’re all good, but I don’t think anyone’s ever going to achieve that Eden, are they, Amy?
[Amy Steagall-Hess] I don’t think it’s achievable, certainly not in an environment like the one that we have here and in a lot of different higher ed institutions. Now, completely different story if you look at the Department of Defense, right? They can implement a zero-trust architecture because they can lock everything down. Their whole goal is to not share data with our adversaries. Our goal here, our mission here, is the complete opposite of that. We are designed by our mission to actually share data and not have everything locked down. We have to be able to collaborate with others across higher ed, across industries, so it doesn’t seem to be a feasible model by definition that we could plug and play here easily.
[Michael Tran Duff] Yeah, I look at it as not necessarily a destination but a journey. So, at Harvard, we laid out our zero-trust framework and our roadmap.
[David Spark] Let me just briefly say, are you further down today than you were a year, two years ago building that out?
[Michael Tran Duff] Absolutely. Yes, butwe laid out a menu of projects that we could work on and if we went through all those projects, it would take probably 10 to 15 years. So, we pick and choose which ones based on the risk and the benefit. So, going back to Andy’s comment, I think that would be very low down in our list.
[David Spark] Yeah, sounds great, but get the other 10 years’ worth of projects done.
Is AI going to help us or hurt us?
7:17.064
[David Spark] This was discussed already heavily on this show, and we’re just going to double down on it right now. So, I’m going to ask both of you, remember that time you easily deployed automation and could instantly reduce your headcount?
[Laughter]
[David Spark] That’s never happened. And by the way, vendors tried to sell this for years. It never, ever happened. But we’ve also heard the doom and gloom of automation, it’s going to come for our jobs. None of it’s come to pass. So, how seriously should we take worries about this new breed of generative AI tools will be coming for cybersecurity jobs soon? I think like what we saw from the last presenter, it’s really just going to amplify what we have. So, the cybersecurity subreddit weighed in with their concerns. Some were sure that current LLMs can’t account for the myriad of dumb things people do. Others already seeing it being used to drive efficiencies, getting rid of lower-level repetitive tasks, while others that use AI tools could automate a lot of current GRC work. So, will AI ever reduce headcount? I do want to get an answer on that one. But if not, beyond what’s mentioned, where are you seeing efficiencies or where are you actually experimenting? And let’s start with you, Michael.
[Michael Tran Duff] I believe, and maybe we’ll have a debate here, the answer is yes. We are in the midst of a new industrial revolution. In prior industrial revolutions, the mechanisms were developed to allow people to be more productive, right? Like when a horse and buggy transitioned to a car. Great, those workers upskilled, and they said, “Sure, I’ll build a car rather than train a horse and build a buggy.” But this revolution is different. Never before have we been able to replace the human mind and the human body with something that’s even more capable and less expensive. So, the market forces are going to drive this. Imagine you have two choices. A human who’s expensive and only works maybe 8 to 10 hours a day in suboptimal versus something that can work for far less, maybe 10% of the cost, 24 by 7. Which one are you going to choose? I believe that’s our future. Not necessarily 5 years, but maybe, I’d say maybe 15 years out.
[Amy Steagall-Hess] So, I disagree.
[David Spark] All right, good.
[Laughter]
[Amy Steagall-Hess] So, I don’t know a security team out there that has too many people right now for the amount of work that they have to do.
[David Spark] Yeah, that is definitely not a problem any security team has.
[Amy Steagall-Hess] No. And so what I think AI brings to the table is the ability for us to alleviate some of the resources that are overburdened right now so that they can focus on the technical specialties that they’ve been focusing on. So, I think it’s going to enhance what we do. It’s going to allow us to provide broader, deeper coverage and better, faster responses. So, we’re using it to enhance our incident response processes to make them as automated as we possibly can. In the world of governance, risk, and compliance, we’re using AI to help us review legal contracts, SOC 2 Type 2s, different documentation that you need to review word by word in order to do a data risk assessment. So, the more we can use AI to do that, we’re going to take care of the backlog that we have, but it’s also going to alleviate what my folks have spent so much time doing, reading line by line by line. We can now have AI do that for us, give us a summary, and we can move on. I don’t think that you can ever get rid of the human oversight and the intuition that is needed to really oversee a lot of this technology. I don’t think we’re going to walk away from that.
[David Spark] Well, I don’t think all of it by any stretch, but there’s no question that AI is trying to replace a considerable amount. But let me ask you just a quick question. Has any employee on your staff expressed any concern that their job would be replaced by AI?
[Michael Tran Duff] Yes.
[Amy Steagall-Hess] No.
[David Spark] Really? They have? What was said?
[Michael Tran Duff] Well, again, and I agree 100% with what Amy said.
[David Spark] All right, so you’re taking both sides of the argument.
[Laughter]
[Michael Tran Duff] Well, it’s based on the timeline.
[David Spark] Okay.
[Michael Tran Duff] So, I think it’s important not to answer this question based on the LLMs of today, which are already smarter than the smartest human who ever lived.
[David Spark] By the way, yeah, and I saw this stuff two years ago and today, and just the speed of growth, as our last presenter said, is astonishing.
[Michael Tran Duff] So, you have to extrapolate out, let’s say, 5, 10 years. I think it’s inevitable that AI will be able to replace a large percentage of today’s jobs. I mean, Sam Altman just a few weeks ago said that superintelligence is only a few thousand days away. So, imagine superintelligence embodied in a humanoid robot. I don’t see anything that it couldn’t do better than a human.
Sponsor – Vorlon
12:21.597
[David Spark] We have a couple of great sponsors, and I want to tell you about one of them, and that would be Vorlon. So, have you ever wondered why data is actually called the new gold? Well, it is, and the reason is because it’s valuable, it’s hard to find, and even harder to protect. Unlike gold though, data doesn’t just sit in a vault. It moves, sometimes on purpose, sometimes by accident, and sometimes it’s plundered by digital pirates, causing serious harm to you, your organization, and your customers. The worst part? Not knowing who took it or what they took. So, third-party APIs make this even trickier. You need to track your data’s journey and manage the secrets that keep it moving. Now that’s exactly where Vorlon comes in here. Vorlon provides continuous visibility into enterprise third-party API landscapes, allowing enterprises to know where data is being transmitted and accessed, and to take action, all without needing an agent. Vorlon, the gold standard for third-party API security. Go check them out at vorlonsecurity.com.
It’s time to play “What’s Worse?”
13:37.613
[David Spark] All right, for those of you who have heard our show before, this is a game we’ve been playing since the very beginning. And the way “What’s Worse?” works is I provide two horrible scenarios, neither one you will like, but it’s a risk management exercise. And by the way, we’re going to want your input of which you think is worse as well. And given that this event is called Showdown at the AI Corral, I asked ChatGPT to come up with some “What’s Worse?” scenarios. Normally, we get these submitted by our audience. So, we’re giving credit to ChatGPT. You’re going to answer first, Amy, on this one.
[Laughter]
[David Spark] And then you will answer, Michael. So, you can agree or disagree. So, here we go. Scenario number one, large-scale ransomware attack. And by the way, I specifically asked it to give me “What’s Worse?” scenarios for higher education, so get ready. A sophisticated ransomware group successfully compromises a university’s IT infrastructure during a crucial period, right before the start of the semester, where thousands of new students are registering, faculty are publishing research, and international students are submitting sensitive documentation. The attack encrypts student data, financial records, and access to critical services like email, online learning platforms, and university’s HR and payroll systems. Sounds bad. Consequences are data loss, research disruption, financial costs, could be paying the ransom, reputational damage, and compliance issues. All right. Sounds pretty bad. What could be worse? Hold on. Let’s hear the second scenario.
[Laughter]
[David Spark] Compromise of a high-profile research project. A nation-state-backed threat actor infiltrates university’s network and targets a high-profile research project involving cutting-edge biomedical research conducted in collaboration with a major pharmaceutical company. The attacker steals sensitive data, including unpublished drug trial results and proprietary methodologies, which they later leak on the dark web. Consequences – intellectual property theft, damaged relationships, national security, litigation and regulatory impact, loss of prestige, and distrust. Amy, which one’s worse?
[Amy Steagall-Hess] Wow.
[David Spark] They’re both pretty horrible.
[Amy Steagall-Hess] They are horrible. I would say that, in my opinion, I think the ransomware one is a tougher nut to crack.
[David Spark] Okay. So, why? Walk me through why that one’s worse.
[Amy Steagall-Hess] Well, there’s just so much more there. I’m thinking through all of the regulatory notifications that we have to make, the reputational damage. I mean, the other one has all of that stuff too. This one’s bigger, broader. It impacts the students. It impacts our HR system. So, all the faculty, all the staff, everybody’s impacted with ransomware.
[David Spark] The only thing that I would argue is I think that number two might have a longer-term impact. That’s the other thing.
[Amy Steagall-Hess] I would agree with that.
[David Spark] All right. So, you’re saying number one is worse. We go throw it to you, Mike. What do you think is worse here?
[Michael Tran Duff] I agree with number one because…
[David Spark] Meaning that is the worse one.
[Michael Tran Duff] It is worse because the level of disruption is much higher than the second scenario.
[David Spark] Okay. So, the level of disruption, so you just think the chaos would be too intense for you to handle. But the second one, let me just throw this. Which ones do you think your lawyers would say would be worse? One or two?
[Amy Steagall-Hess] Arelawyers here?
[David Spark] Are there any? I know I talked to a lawyer earlier. There is a lawyer in the room. What do you think the lawyers would say? I’m thinking number two they would say is worse.
[Michael Tran Duff] I still go with number one.
[Amy Steagall-Hess] I still think number one.
[David Spark] Number one. All right. We’re going to throw this to the audience. So, to remind you, first scenario, large ransomware attack that just disrupts the beginning of the semester, just explodes it, or high-profile research project that gets involved with a huge pharmaceutical company that has…and from a nation-state attack, I should mention. That’s key. We’re talking this is at federal level here. So, by applause, how many people think it’s worse, scenario number one, ransomware attack? By applause.
[Applause]
[David Spark] All right. And now, same. By applause, how many people think the second scenario, the high-profile research project getting hacked, is worse? By applause.
[Applause]
[David Spark] All right.
[Amy Steagall-Hess] I think we win, David.
[Michael Tran Duff] David, can I add one more reason?
[David Spark] Sure, throw it.
[Michael Tran Duff] On number two, you said a key thing there, nation-state actor.
[David Spark] Yeah.
[Michael Tran Duff] I think we all…
[David Spark] That puts a huge lens on you, an enormous lens.
[Michael Tran Duff] It does, but they’re also the hardest to protect against. So, I think there’s a level of understandability there.
[David Spark] So, now are you switching your answer?
[Michael Tran Duff] No, no, no. No, I’m saying number one.
[David Spark] All right. Cool.
What is Dave’s mom talking about?
18:29.007
[David Spark] All right. This game is pretty much that title right there. I interviewed my mom. It’s going to be a shock. She’s not a cybersecurity expert. But she’s a good sport, and she plays along with the stupid ideas that I come up with. So, I’m going to do these varying degrees of difficulty. If my guests can’t get these ones correct, I will throw it to the audience. So, understand, I read some term in cybersecurity to her, and she tries her best guess effort to explain what it is. I will give you a huge hint. In the first case, she actually gets it right, and then varying degrees of right after that, or completely wrong. All right? So, you have to, in some cases, do reverse logic. Like if I was hearing this for the very first time, and I didn’t know anything about cybersecurity, how would I explain it? All right? So, first one, let’s see if you can get this one.
[Dave’s mom] One team functions as an adversary so that others know how to protect themselves.
[David Spark] What is that?
[Michael Tran Duff] I’d say red teaming.
[Amy Steagall-Hess] Red teaming.
[David Spark] Red teaming, very good. Okay. Good job. Now they get hard. Here you go.
[Dave’s mom] Well, frankly, if it’s in my house, I want to squish it and get rid of it. But I think it’s something that’s insidious in technology.
[David Spark] What is my mother talking about?
[Amy Steagall-Hess] A bug.
[Michael Tran Duff] Bugs, yeah, software bugs.
[David Spark] Okay. You’re very close. It’s not a bug though. We’re talking cybersecurity.
[Michael Tran Duff] Viruses.
[David Spark] You’re very, very close.
[Amy Steagall-Hess] Malware.
[David Spark] No. But when she says I want to squish it, that’s kind of a key thing to think about there. Because bug was a good first answer, but that’s not it. Take one more stab and I’m throwing it to the audience if you can’t get this one.
[Michael Tran Duff] I think we need help.
[David Spark] We need help. All right. I’m throwing to the audience. Who thinks they know what it is?
[Audience member] A worm.
[David Spark] Worm. Correct! Bob, you got it right there. Worm. Very good. Okay. Good job.
[Applause]
[David Spark] All right. Here comes the next one. This one’s tough, I’m going to be honest, this one’s tough.
[Dave’s mom] When you try to act like your organization is impenetrable.
[David Spark] All right. The last two were she kind of knew what she was talking about. This one is off, I will just say.
[Laughter]
[David Spark] I will say it’s pretty off. I can play it again for you. Hold on. Listen.
[Dave’s mom] When you try to act like your organization is impenetrable.
[Michael Tran Duff] Your mom’s quite the riddler.
[Laughter]
[David Spark] I will say… I’ll give you a hint. Think of a term that may sound a little conceited.
[Michael Tran Duff] We were talking about zero trust earlier.
[David Spark] No. This one’s tough.
[Amy Steagall-Hess] And it’s a cybersecurity term.
[David Spark] It is a cybersecurity term. I’m going to throw this to the audience. Again, work off my hint here. It’s a term that kind of sounds a little conceited, hence why she said what she said. Anyone want to take a stab at this one? Hoover?
[Audience member] [Inaudible 00:21:19] power?
[David Spark] No. I’m going to give this. This is going to be too tough for people. Security posture management.
[Michael Tran Duff] Okay.
[Amy Steagall-Hess] Oh, wow.
[David Spark] There you go. Okay.
[Amy Steagall-Hess] Wow, Mom.
[David Spark] Okay, all right, all right. The very last one. Here we go, the last one. Again, this one she gets 100% off. All right? But, again, do the reverse logic. You’ll be able to figure it out. Okay?
[Dave’s mom] When nothing happens, and you’re bored to death.
[Laughter]
[David Spark] What is she talking about?
[Michael Tran Duff] Simulated fishing?
[David Spark] No.
[Laughter]
[David Spark] Nothing happens, and you’re bored to death. Again, I just mention. And you definitely know this term very well.
[Amy Steagall-Hess] Resilience?
[David Spark] No. Okay.
[Amy Steagall-Hess] Not even close.
[David Spark] Anyone want to take a stab at this one? Here, let me play it one more time.
[Dave’s mom] When nothing happens, and you’re bored to death.
[David Spark] Anyone take a stab?
[Audience member] [Inaudible 00:22:13].
[David Spark] Hold it, someone, I might have heard this. What’d you say out here?
[Audience member] Zero day.
[David Spark] Zero day. Correct!
[Amy Steagall-Hess] Zero day.
[Laughter]
[Applause]
[David Spark] Good job.
[Michael Tran Duff] See? It was a zero day.
[Michael Tran Duff] That’s a former member of our team who’s very wise.
[Laughter]
[David Spark] Good job.Knows my mom very well.
How is the CISO role evolving?
22:37.845
[David Spark] Do CISOs know what they’re doing? This is an attack on the two of you right there.
[Laughter]
[David Spark] So, over on the cybersecurity subreddit, the question came up from someone whose interactions with the CISO was a nightmare, who didn’t understand the simplest concept or know the first thing about computers, networks, or IT in general, and acted as a project manager who just spouted buzzwords to the board. Others pointed to the complete opposite problem. With highly technical CISOs micromanaging teams, these are two extremes, but CISOs are not immune from imposter syndrome. We were talking about this. Most CISOs I’ve spoken to admit to repeated bouts of imposter syndrome. I’ll ask, have either of you been challenged in your competency as a security leader? And while you may still feel imposter syndrome from time to time, what was the moment that things started to click for you as a security leader? Amy, I know you’ve got an answer for this.
[Amy Steagall-Hess] So, yes, I’ve been challenged multiple times, not just in higher ed, but in my former life in the military as well. And every time it happens, I used to think, “Wow, what a jerk.”
[Laughter]
[Amy Steagall-Hess] But I really started to reflect on, okay, why is this happening? There have been distinct moments in my career where I wholeheartedly felt this has nothing to do with my technical capabilities. It’s either this person has some insecurities in themselves and they’re projecting that on me, and there have been other times where I wholeheartedly believe that it was solely because I was a woman, and I was in a role in which they didn’t think that I should be in. When that happens, this little imposter syndrome gremlin jumps on your shoulder and starts chirping things into your ear. And that’s what then starts replaying over and over in your mind and you start to doubt yourself and you start to doubt your confidence. And I will tell you that one thing that actually, Michael, a few years ago, you gave me advice, and you said – I don’t know if you remember this – but you actually said to me, “Always remember, you’re the expert in the room.”
And at the time, I had no idea what he meant by that because it was one of these conversations where I was doubting my capabilities. I started reflecting on that, and I actually tell myself that a lot when I go into a situation, “You are the expert in the room.” Being the expert in the room doesn’t necessarily mean that you’re the smartest person in the room. Being the wisest person in the room typically means that you know you’re not the smartest person in the room. Being the wisest person in the room means you’re there to learn something from everybody else that’s in the room. And that’s really when I started thinking about this in a different way and knocking that little gremlin off my shoulder and just talking to myself and saying, “Look, you are confident. You bring 30 years of experience to this role. That alone means you’re the expert in the room.”
[David Spark] All right, Michael, I’m going to throw this to you. And I’ll just preface it with do you feel you would have not had imposter syndrome if you went to a community college after this?
[Laughter]
[Michael Tran Duff] Well…
[David Spark] Also, I got to imagine that on top of just being in cybersecurity, you’re also working, both of you, for these enormous, well-known, incredibly intelligent institutions. That’s got to weigh on you on top of it. Yes?
[Michael Tran Duff] Absolutely weighs on you. But I’ve never doubted my InfoSec competency or judgment. And I believe it’s important for us to understand the technical underpinnings of the work. That said, there’s much more to it. The technical side’s the easy part. A CISO needs to be a great leader, and I’ve doubted my competency as a leader often.
[David Spark] Hold it, wait, wait. Let’s pinpoint. Give us a moment that you doubted it.
[Michael Tran Duff] All the time.
[David Spark] But what happened that made you feel that?
[Michael Tran Duff] Well, the question in my mind is always, “Am I a good enough leader to be a good and successful CISO?” And that happened over a long period of time. So, I immersed myself in tons of mentoring and coaching and internships and readings and listening to feedback and acting on it. And I’m still on that leadership growth today. It’s so funny, and I want to ask Amy to look at something on my notes here. Because one of the key moments in my time here at Stanford was I was going into my first board presentation, and the person who hired me said, “Michael, I want you to remember that you’re the expert in the room.” And that gave me the confidence to do it. So, I passed along that advice.
[David Spark] So, there you go. That’s good pass-along advice.
[Laughter]
[David Spark] Oh, Jesus. First time we’re getting crying on the show.
[Laughter]
Unexpected outcomes or failures?
27:45.722
[David Spark] Jim and Pam, Niles and Daphne, Ross and Rachel. There’s been a lot of iconic “will they, won’t they” moments in our cultural lives. And now, get ready for this, there’s the federal government and a comprehensive federal privacy law. Almost exactly the same. Will they or won’t they? So, over the summer, there was a glimmer of hope that the American Privacy Rights Act might pass, but that now seems like it’s been put out to pasture. Still, the drumbeat of state privacy laws means there is some momentum to get a federal law on the books.
So, besides it being the nice and right thing to do, why should businesses get ahead of the curve with privacy? Businesses don’t have a history of behaving altruistically en masse, I will say. So, it took the EU’s GDPR regulation for US companies to start taking privacy seriously, noted Apu Pavithran in a piece on Dark Reading. He suggested that organizations create an actual data protection plan now, as well as possibly bring on a data protection officer with training for employees who interact with consumer data. So, I’m going to throw this to you, Michael, because you are a data privacy officer on top of being a CISO. What would be the compelling argument you could give, or other CISOs can give actually, to get buy-in for being proactive with data security?
[Michael Tran Duff] Right. Well, I would start with the first part of my argument is that, as you already alluded to, David, we’re already subject to a patchwork of state and international privacy laws today. We’re already there. But privacy is much greater than compliance. Compliance is the floor, the bare minimum. To me, privacy is a matter of ethics. It is about doing the right thing, and we want to make sure that we are good stewards of personal information. So, that’s my do the right thing argument. Okay, argument number two. Let’s ask ourselves a couplequestions. When there’s a data breach, is that a privacy incident or is it a security incident?
[David Spark] By applause, how many think it’s a privacy incident?
[Applause]
[David Spark] All right. For the people raising their hands, explain to the other people that… And how many people think it’s a data security incident?
[Applause]
[David Spark] All right. So, more people think it’s data security than privacy.
[Michael Tran Duff] And can I ask for one more round of applause? How many think it’s both?
[Applause]
[David Spark] There you go. All right.
[Michael Tran Duff] Exactly. Now, let’s take it one more step further. Is preventing that incident, is that a privacy matter or is that a security matter?
[David Spark] People, I’m seeing more security or both.
[Michael Tran Duff] It’s both. It’s both. Right?
[David Spark] All right. It’s both. So, that’s how you negotiated both titles when you went to Harvard.
[Michael Tran Duff] Yeah.
[Laughter]
[Michael Tran Duff] And that is part of it, actually. So, at Harvard, we’re taking the progressive approach of combining privacy and security into a single program where they can act in concert and on equal footing. We’re calling it PrivSec, and I believe it’s the way of the future because privacy and security are largely overlapping, they’re highly complementary, and they’re increasingly inseparable.
[David Spark] All right, your view, you haven’t been able to negotiate to get the data privacy officer, have you, yet?
[Amy Steagall-Hess] So, actually, Stanford does have a new chief privacy officer.
[David Spark] What am I saying? I just met the privacy officer.
[Amy Steagall-Hess] You did just meet him.
[David Spark] Take that back. He’s in this room somewhere. Where is he? Applaud. Raise your hand. Where is he? He’s somewhere. Oh, he’s not here. He’s ignoring you, Amy.
[Amy Steagall-Hess] [Laughter]
[David Spark] Oh, not good.
[Amy Steagall-Hess] I’m sure he’s doing some very valuable work outside of this room.
[David Spark] There you go, all right. He’s waiting till November 12th when this episode drops. All right.
[Amy Steagall-Hess] And so we’ve taken a different approach here at Stanford. We’ve actually split the privacy and the security functions apart from each other, and there’s a lot of reasons for that. One, we have minimal resources. Having everyone have to do everything all of the time is a burden that I really wanted to alleviate, and I wanted to develop very specific roles and responsibilities so that we could grow experts in specific areas. I also wanted to make sure that there was no conflict of interest, and at times, when you’re wearing both of those hats, I truly believe that there could be a conflict of interest. And so I appreciate having a partner, a chief privacy officer, that we can bounce things off of each other, we can debate about how we’re going to handle something, and we can look at it from two different lenses, which I think is really important. As you all have said, it’s both at times, and I like to have that sounding board to bounce things off of.
[David Spark] And, Michael, you’ve got split personality, so that’s not necessary, right?
[Laughter]
[Michael Tran Duff] Well, yeah. If I could just… And that’s absolutely valid. And that is the debate about combining or not.
[Amy Steagall-Hess] There is no wrong answer.
[Michael Tran Duff] Yeah. But think about this. So, at Harvard, I have a 45-person information security team. Not bad for higher ed. And I have a 45-person privacy team, which is unheard of just about anywhere. These are the same 45 people, right? But imagine that. Imagine a 45-person…
[David Spark] Did you have to double their salary?
[Michael Tran Duff] Nope.
[David Spark] No?
[Michael Tran Duff] No, in fact…
[David Spark] Oh, they got screwed.
[Michael Tran Duff] I mean, we talked about it as a team, and they were very excited to learn about privacy. And I said, “Look, I want everyone on our team to be as marketable as possible.” What are two of the most marketable skills today? Privacy and security.
Sponsor – Wiz
33:38.950
[David Spark] So, we do have another wonderful sponsor, and that would be Wiz. Wiz transforms cloud security for customers, including 40% of the Fortune 100 – I can do the math there, that’s 40 of them – by enabling a new operating model. Now, Wiz CNAPP empowers security and development teams to build fast and securely by providing visibility into their cloud environments. With Wiz, organizations can prioritize risk and stay agile. For more, just go to their site, wiz.io.
It’s time for the audience question speed round.
34:20.920
[David Spark] All right. I have in my hand right here questions from our audience. I asked them to provide some questions. And we have a good amount of time, so I think we might be able to get through all of these. This one comes from Tim Collier, who works here at Stanford. This question is for you, Michael. What’s the big difference between being a CISO at Harvard versus Stanford? And by the way, be very careful about your answer here.
[Laughter]
[Michael Tran Duff] I know. I have many answers to that that I probably can’t share right now.
[David Spark] You have one for a Harvard audience and one for a Stanford audience, I’m sure.
[Michael Tran Duff] That’s true. They’re 95% the same, both top research universities. I do think it’s interesting that there’s a cultural difference. Here, there’s more of the Silicon Valley culture. At Harvard, there’s more of the New England culture. One’s not better than the other, but they are slightly different. Most of the differences are very minor. I won’t get into some financial, the way some finances are handled. But I’m looking over at my former boss, Steve Gallagher, and he knows this. But I just have to share that at Stanford, there’s this thing called SGG. It’s a bucket of one-time money. And when I was here, it was about 7 million a year, which is great, sounds good, that gets divvied up as requests come in. At Harvard, it’s 40 million, and it’s growing to 55 million over the next few years.
[David Spark] Stanford’s got to catch up, don’t they?
[Michael Tran Duff] Yeah. So, that’s enabled us to do a lot of things that we wouldn’t otherwise be able to.
[David Spark] All right. Again, this question comes from someone who’s trying to break into cybersecurity, and he’s just being a sponge right now, just absorbing as much as he can. It’s Jonathan Rodriguez, who studied over at Cyversity, and he actually left the gaming culture to join cybersecurity. So, welcome. We love the fact you’ve done that.
[Amy Steagall-Hess] Nice.
[David Spark] So, I’m sure we can go on and on about this, but I just want your snap answer to this question. Why, with all the tools we have available to us, why do we still feel like we’re constantly playing catch up?
[Amy Steagall-Hess] It’s interesting because you can have all the tools in the world. If you don’t have the people to actually run the tools, do the analytics…
[David Spark] We had the discussion yesterday. You got the money for the tool, but not the person.
[Amy Steagall-Hess] Exactly.
[David Spark] What’s the point?
[Amy Steagall-Hess] You can get the money for the tool, you can buy the tool. But the FTEs that you asked for to run the tool, well, you don’t get that funded. So, then there’s a problem. So, oftentimes, you have tools running in the background, but you really aren’t utilizing them to their fullest capabilities. So, you’re investing in this product, but you can only turn maybe three of the capabilities on because that’s all the amount of staff that you have to actually run the tool efficiently.
[David Spark] All right. Michael, what do you think?
[Michael Tran Duff] Well, I think it’s sometimes discouraging to realize that we are trying to solve the same problems in cybersecurity that have existed since nearly the beginning of computing.
[David Spark] Mm-hmm.
[Michael Tran Duff] But I do believe that finally, for the first time in history, we have the tools necessary to solve them. Passwordless will help solve the phishing problem. Going serverless. I think AI is currently more of a foe than a friend, but I think is ultimately the key to solving cybersecurity.
[David Spark] All right. Here, this is a good question. It comes from Lo Smith of Harvard, who was on this very stage. And we just talked about this, about privacy, but I want to know philosophically, when you’re explaining this to people, what does it mean to be privacy forward? This is up your alley.
[Michael Tran Duff] Well, I’m biased on this one because I think that, again, I believe privacy and security are inseparable.
[David Spark] Mm-hmm.
[Michael Tran Duff] And I believe everything we do in security has a privacy component to it, and vice versa. So, by being privacy forward, we incorporate privacy into everything we do. I know Stanford has a set of privacy standards, and you’ll notice that Harvard now has a very similar set of principles. So, a strong privacy program begins with a strong, firm foundation of privacy principles. So, I think just incorporating that into everything we do.
[David Spark] What do you think, Amy? What does it mean to be privacy forward?
[Amy Steagall-Hess] Well, I think it’s important to incorporate privacy into everything that we do. And for a long time, I think we were focused very much so on the security side of the house, but as we know, there’s not a student out there that’s not worried about their privacy right now. There is not a board of trustee member that’s not worried about the privacy of every individual on this campus. And so I think putting privacy out there in the forefront where you’re thinking about it when you’re building your tooling, when you’re building capabilities, that’s what being privacy forward means, putting it at the forefront.
[David Spark] All right. Two more questions here. This comes from Biniam Debrezion, also at Stanford. What’s one aspect of the AI capabilities – and again, there’s a lot here going on – but what’s the one that concerns you the most right now?
[Amy Steagall-Hess] Wow, there’s so much that concerns me with AI, but the biggest concern that I have right now is how pervasive it is in our environment and that we do not have our arms wrapped around it.
[David Spark] Contributing and listening to the CISO Series Podcast…
[Amy Steagall-Hess] We don’t have control over a lot of the platforms…
[Applause]
[Amy Steagall-Hess] …the tools, the apps, the plug-ins, the add-ins that are out there. And so we don’t know what we don’t know. So, we don’t know what’s out there scraping our environment because we don’t know who implemented it in our environment. So, to me, it’s just how big it is, how much of it is out there, and how pervasive it is. And you can implement something into an environment, and it’s reading everything in your Google Drive. It’s reading everything in your e-mail. It’s scraping data. And if we haven’t had the chance to look at it, to do a proper review and approve it, we definitely have some vulnerabilities out there.
[Michael Tran Duff] I would say the number one, I’ll use the term, PrivSec risk today worldwide is social engineering. That includes phishing. And I think you may have heard in the presentation prior to this that AI is enabling that form of attack. So, that’s my biggest concern today. And maybe include in that deep fakes, that you can pose as someone else and have them say anything you want them to say, which could cause some mass disruption. That’s what I’m worried about today. Longer term, I have different concerns.
[David Spark] All right. All right. My last question here, and this comes from someone from Apple who wished to stay unnamed, and you will know in just a moment. When you’re validating two devices, let’s just say PC and Apple, and one is definitely less secure, how do you rationalize onboarding it?
[Laughter]
[Michael Tran Duff] Is that going to me first, David?
[David Spark] Go ahead. Jump in.
[Amy Steagall-Hess] Sure, Michael. Let’s hear.
[Michael Tran Duff] Okay. I think this is actually a great topic to bring up because the work that we all do in security and privacy is an imperfect… We’re in an imperfect world, and we are always juggling all these different risk factors. And it’s just we have to be pragmatic. It is not pragmatic at Stanford or Harvard to say, “Guess what? You can only use Apple devices.” It’s just not going to happen. So, we have to accommodate those needs, and we have to mitigate those risks. So, we may need to more heavily fortify those devices that some want to use.
[Amy Steagall-Hess] Yeah, I think it’s all about a balance there, especially in this environment where we can’t just issue the device that we can harden to every single one of you, and that is what we do our work on.
[David Spark] But don’t you, at a certain point, just say… I mean, you’re getting a PC or you’re getting a Mac or whatever the heck you’re… I don’t know. How does it work? Or do people get a choice of what they want?
[Amy Steagall-Hess] You get a choice.
[David Spark] Oh, you do? Okay, good.
[Amy Steagall-Hess] You can bring your own device and do your Stanford work on it. Now, we do have security controls that you are supposed to have in place per our policy. But at the same time, we can’t mandate that you only use one type of device. It’s just not going to work in this environment. We can’t afford it, certainly, because that would mean we’d have to issue the device that we have deemed appropriate, and I won’t say which one.
[Laughter]
[Amy Steagall-Hess] But we would have to issue that to each and every one of you, and there’s just significant cost in that that we wouldn’t be able to sustain.
Closing
43:21.805
[David Spark] Well, that brings us to the very end of this show. Let’s hear it for my guests!
[Applause]
[David Spark] It’s Amy Steagall-Hess, who’s the CISO over here at Stanford. The former CISO of Stanford, but now the CISO and data privacy officer over at Harvard, it’s Michael Tran Duff. Let’s hear it for Michael!
[Applause]
[David Spark] And let’s also hear it for our phenomenal sponsors, that’d be Wiz and Vorlon. Thank you so much for supporting us. Remember, you can go to their sites, wiz.io and vorlonsecurity.com. Check them out for cloud security and API security needs. Just any last thoughts from either of you? I believe one of you is hiring currently, yes? What’s the story?
[Amy Steagall-Hess] Yes, the Information Security Office is hiring, so we’re very fortunate to be looking for a cloud security engineer and a security operations engineer. Really excited about it.
[David Spark] And I noticed when you walked in here, Michael, the number of people who saw you were so excited to see you again. So, you are very much missed on this campus. It’s pretty clear.
[Michael Tran Duff] Well, I miss everyone here. And going back to our very first question about big mistakes, the only reason I haven’t made more mistakes is because I’m looking at all the reasons right here. It’s all the friends and colleagues and leaders and mentors and coaches that guided me along the way. So, thank you.
[David Spark] All right. We will hug after the show.
[Applause]
[David Spark] All right. Thank you very much. Thank you, audience. Thank you, Stanford University. You could not have been kinder to me. We greatly appreciate you all contributing and listening to the CISO Series Podcast.
[Applause]
[Voiceover] That wraps up another episode. If you haven’t subscribed to the podcast, please do. We have lots more shows on our website, CISOseries.com. Please join us on Fridays for our live shows – Super Cyber Friday, our virtual meetup, and Cyber Security Headlines Week in Review. This show thrives on your input. Go to the Participate menu on our site for plenty of ways to get involved, including recording a question or a comment for the show. If you’re interested in sponsoring the podcast, contact David Spark directly at David@CISOseries.com. Thank you for listening to the CISO Series Podcast.